DevOps Consulting, Cloud and Website Security Services
Cloud hosting, deployment and security that stay out of your way.
Overview
The best product still fails on shaky infrastructure.
We set up cloud, deployment and security so releases are fast and boring, costs stay under control, and the whole thing is monitored and hardened against the threats that matter.
Who this is for
Sound familiar?
Deploys are manual, scary, and happen on a Friday at nobody's request
Your cloud bill grows and nobody can explain which service did it
You are being asked security questions you cannot currently answer
What we actually do.
Four ways in
Cloud setup and migration
AWS, Google Cloud or Azure set up, sized properly and moved without downtime.
Automated deployment
Push a change and it goes live safely, with a one click way back if it breaks.
Security and backups
Access control, SSL, patching and backups you have actually restored from.
Monitoring and support
Alerts the moment something breaks, and someone who knows what to do about it.
Capabilities
Everything this covers.
Ask for one of these or all of them. It is the same team either way.
- AWS, Google Cloud and Azure setup
- Cloud migration
- CI/CD pipelines
- Infrastructure as code
- Docker and Kubernetes
- Server management and hosting
- Database administration
- Backup and disaster recovery
- Monitoring and alerting
- Security hardening and audits
- SSL, WAF and DDoS protection
- Access and secrets management
- Cloud cost optimisation
- Incident response
Not seeing the exact thing you need under Cloud, DevOps & Security? It is almost certainly still us. Tell us the problem and we will say plainly whether it is ours to solve.
How it runs
Four steps. No mystery.
Every step has an owner and a date. You always know which one we are on, and what has to be true before the next one starts.
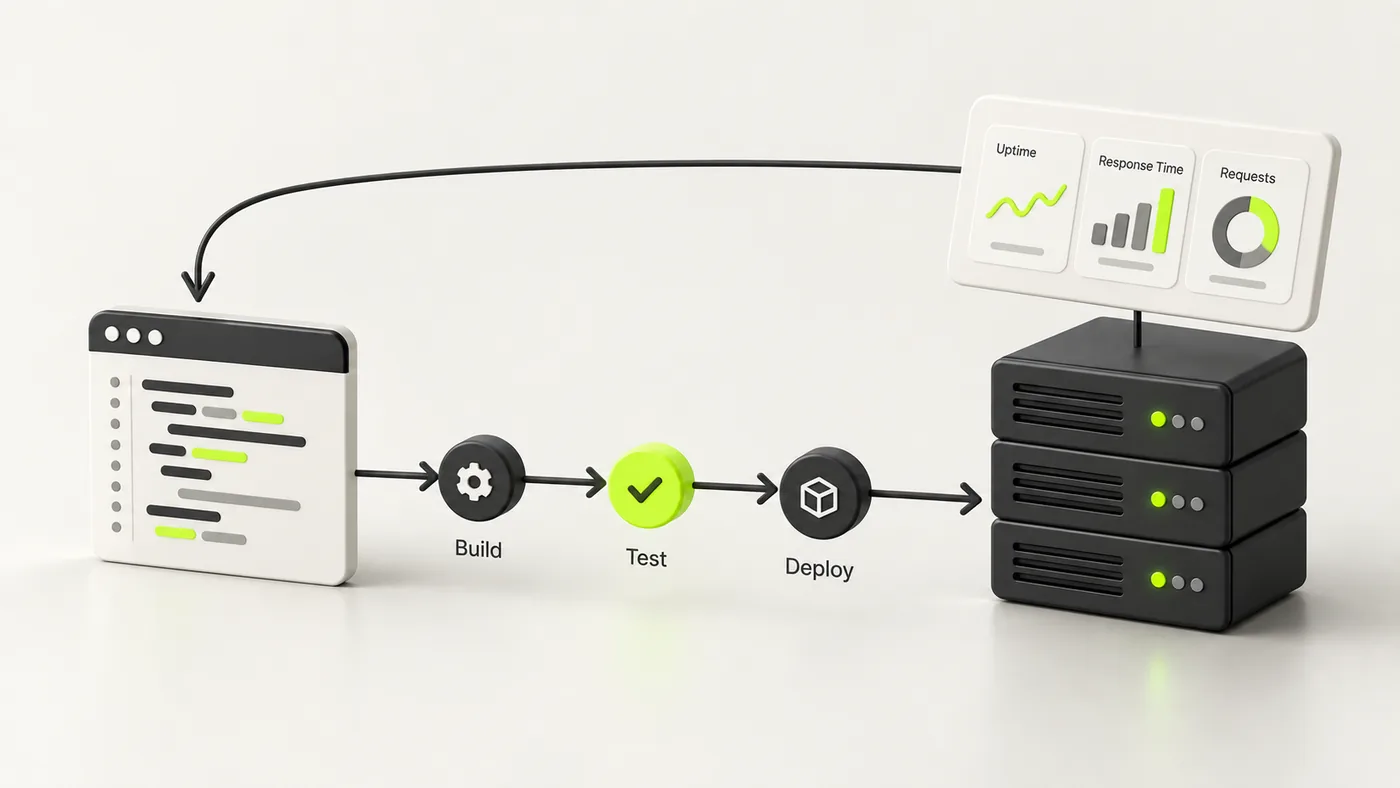
Audit
What is running, what it costs, who can reach it, and what happens today if the main instance disappears.
Automate
Infrastructure as code and CI/CD, so a deploy is a routine, reversible, boring event rather than an occasion.
Harden
Access control, secrets management, backups and network boundaries, tightened to what the workload actually needs.
Observe
Metrics, logs and alerts that tell a human something is wrong before a customer does.
Deliverables
What lands in your hands.
Yours at the end of the engagement, whether we carry on together or not. Nothing here is held hostage.
Infrastructure as code
Terraform repoYour whole environment described in files, so it can be rebuilt, reviewed and rolled back like any other code.
CI/CD with automated rollback
PipelineDeploys become routine and reversible. A bad release goes back without anyone panicking.
Cost breakdown and right sizing plan
ReportWhere the bill actually goes, service by service, and what to switch off or resize first.
Secrets management and access policy
Vault + policyCredentials out of code and config, with who can reach what written down and actually enforced.
Backup and restore, tested
Documented + provenBackups you have actually restored from, because an untested backup is a guess with a filename.
Monitoring, alerting and on call runbook
Dashboards + runbookAlerts that wake a human for real problems only, and a page telling them what to do when it happens.
- AWS
- Docker
- GitHub Actions
- Terraform
- Nginx
- PostgreSQL
- Cloudflare
- Grafana
Outcomes, not activity.
What you get
- 01
Deploys that take minutes, not evenings
- 02
A cloud bill you can actually explain
- 03
Backups that have been tested, not assumed
- 04
Alerts before your customers notice
Live proof
Cloud, DevOps & Security we have shipped.
Go deeper
Specialist cloud, devops & security services
Working with us
Four things you can hold us to.
- 01
A real reply within one business day
From a person who read your brief, not a ticket queue.
- 02
The people on the call build it
No account manager relaying messages in between.
- 03
Tracked from first click to booked call
Every enquiry traced to the page and search that brought it.
- 04
No hostage code. It is all yours.
Code, domain and accounts in your name. Take it in house whenever you want.
FAQ
Cloud, DevOps & Security questions.
AWS, Google Cloud and Azure. We recommend based on your workloads, existing stack and budget rather than a single default.
Yes. We often start by adding CI/CD, infrastructure as code and monitoring to your current setup, then modernise where it pays off.
Yes. We set up observability and alerting and can provide 24/7 coverage so problems are found and fixed before users notice.
A check of everything an attacker would try first: outdated software and plugins, exposed admin panels, weak authentication, misconfigured servers and storage, missing security headers, leaked secrets and how backups are handled. You get a report ranking each finding by risk, with the fix written next to it, and we can close the issues for you rather than leaving you with a list.
If you store customer data, take payments or sell to larger companies, yes, at least once a year and after major changes. A penetration test is a controlled attack by people trying to break in, and it finds what automated scanners miss. For a smaller site, a security audit plus hardening often gives most of the protection for less money, and we will say which one you need.
No, and we usually advise against it. Migration is expensive and rarely the actual problem. Most of the gain comes from automating deploys, putting infrastructure in code and getting monitoring in place, all of which we can do on whatever you are running now.
By finding what is running that nobody uses, right sizing what is oversized, and moving predictable workloads onto committed pricing. The first audit usually finds idle resources and over provisioned instances, which is the cheapest saving available because nothing has to be rebuilt.
It means metrics, logs and alerts are configured so a real problem pages a human at any hour, with a runbook saying what to do. We set that up as standard. Whether we are the humans on the end of it depends on the support agreement, and we will be clear about which one you are buying.
That depends on what they ask for, and the questionnaire is usually the fastest way to find out. We cover the foundations that most of them test: access control, encryption, secrets handling, backups, logging and patching. Formal certification such as SOC 2 is a separate programme, and we can prepare the technical side of it.
Related services